Cybersecurity and AI

ACN: ‘AI makes attacks more dangerous; let’s use it to defend ourselves, but with caution’

Massimo Marotti, Director of the Strategy and Cooperation Service, explains the current context of hybrid wars and the use of artificial intelligence

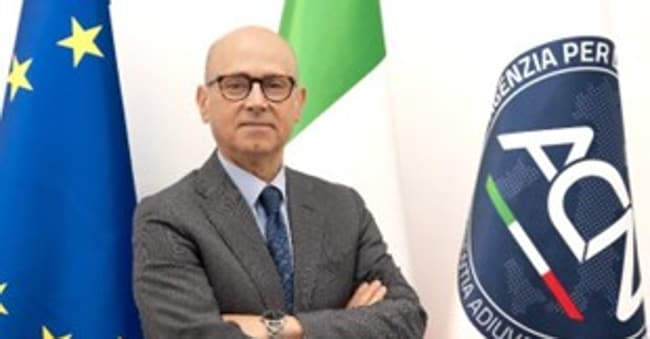
L'ambasciatore Massimo Marotti, direttore del Servizio Strategie e Cooperazione di Acn

4' min read

Translated by AI
Versione italiana

4' min read

Translated by AI
Versione italiana

(Il Sole 24 Ore Radiocor) – The use of AI tools ‘will increase the scale of attacks, but at the same time, the capacity for early defence has also grown’. Ambassador Massimo Marotti, director of the Strategy and Cooperation Service at the ACN, takes stock of the increasingly crucial role of artificial intelligence in cyber security. His advice – particularly in light of the current warnings aimed at slowing down the development of AI – is to use it “with caution and a critical eye”, he explains in an interview with DigitEconomy.24, in collaboration with Digit’Ed, a group active in training and digital learning.

Cyber incidents are on the rise – should we expect this trend to continue in the current geopolitical climate? 

Loading...

The accident figures show an upward trend, but this is also due to the increase in the area monitored by the Agency under the NIS2. Today, there are over 20,000 public and private organisations required to report accidents.

How is the landscape changing with the use of AI? Is it becoming more difficult to defend against cyber attacks?

The current system is, in fact, disrupted by the use of artificial intelligence because, whilst the techniques and methods of attack remain essentially the same, the speed, scale and economics behind the attackers have changed. In other words, many of the attacks that previously required preparation and sophistication are now much simpler to carry out, thanks to artificial intelligence models. Furthermore, the more attackers use artificial intelligence models, the greater the scale and danger of the attacks.

Is the regulatory framework adequate? 

A constituency has emerged on this issue, both nationally and internationally. However, the threat has evolved constantly over the past decade, and legislation has not always been able to keep pace with developments in technology and criminal behaviour. Regulations have been proposed, such as the CADA (Cloud and AI Development Act), which is currently under negotiation. These are all tools designed to link existing regulatory frameworks, which need to be adapted in light of interactions with artificial intelligence and cyber security.

 Is Cada heading in the right direction?

Yes, although there are some adjustments to be made, and we will be proposing them. It is difficult to predict at this stage what the final outcome will be, but the approach being followed is the one that has been in place for some time: it is a collective endeavour involving the 27 Member States. That said, the following remains true: technological developments are outpacing our ability to regulate.

So how should we respond?

Loading...

We also normally make use of other tools, such as international cooperation and the development of technical standards. The defence response, therefore, is a mix of European or national regulatory instruments, codes of conduct, and the sharing of methods, practices and information. For example, ransomware has grown in recent years, but so too has collaborative activity to defend against ransom demands. The informal group of countries, the Counter Ransomware Initiative, promoted by the United States, now comprises 80 countries. They exchange information on how to respond to the phenomenon and limit its impact. Interpol, Europol and the European Commission are all involved in this collaboration.

So, is the key to strengthening cooperation between countries and between the public and private sectors? 

Collaboration with the private sector has become – and remains – the way forward. With regard to common standards, for example, within the G7 we have been working to define the best ways to certify the safety of artificial intelligence models. This joint effort has given rise to a project aimed at enhancing the transparency of software and components within artificial intelligence systems. We have reached a consensus amongst the seven countries and the European Commission, which will also serve as a guide for the private sector. In this way, we are all working to the same method, using the same verification techniques.

Private individuals, however, are predominantly foreign..

Yes, we do not have any artificial intelligence providers in Italia, but we are committed to and working towards developing European capabilities. The Commission itself has a plan and funding to develop this capability, starting with start-ups and making use of the computing power available in Europe. The hope is that industrial and manufacturing enterprises can be developed within the European legal framework.

As AI has increased our ability to attack, is our ability to defend also increasing?

We are facing a phenomenon that cannot yet be quantified; the use of AI tools will increase the scale of attacks, but at the same time, the capacity for early defence has also grown. Technology has evolved to the advantage of attackers, but it has also evolved to the advantage of defenders. What is still needed is to fully implement the use of artificial intelligence for defensive purposes as well. We are developing this; this marks the beginning of a new phase.

A final suggestion for improving the response to attacks? 

We need to raise individual awareness. It is not simply by setting the alarm at home that we can prevent a burglar from getting in; we must also ensure that the door is secure and that all members of the family take the same care and are equally vigilant when they go out. Leaving the metaphor aside, our systems are currently vulnerable and require everyone’s attention. Greater widespread awareness should enable us to improve our overall capacity – as a country and as a group of allied nations – to manage risks. And finally, as mentioned earlier, it is essential to utilise AI for cyber security.

Recently, a number of warnings have been issued calling for a slowdown in the use of AI..

Yes, we need to be cautious and approach it with a critical eye. This will help us gain a better understanding of the different types of attacks. The range of possible malicious actions is so vast that preventative measures must also be on an equal footing.

Copyright reserved ©
Loading...

Brand connect

Loading...

Newsletter

Notizie e approfondimenti sugli avvenimenti politici, economici e finanziari.

Iscriviti