Interview

Cyberattacks: Mastrapasqua says, ‘Older systems are the most vulnerable; we need to focus more on cybersecurity’

Mastrapasqua, president of Assocold: “Remote monitoring helps to mitigate these risks, but we need to raise the bar across retail networks”

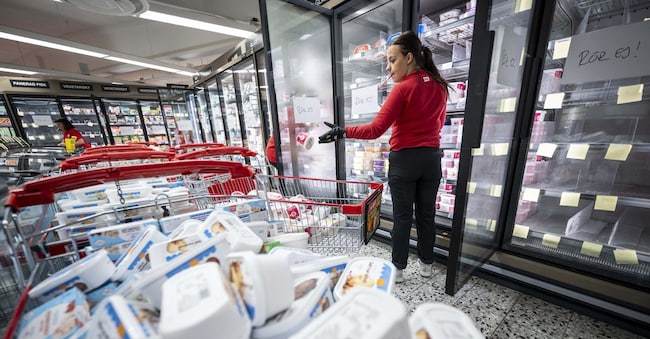
 16878

3' min read

Translated by AI
Versione italiana

3' min read

Translated by AI
Versione italiana

‘Remote monitoring of refrigerated display cabinets is not the problem. In fact, to a large extent, it is the solution, precisely to prevent such attacks. These attacks are facilitated in this case by IP access points in the retail outlets’ networks that are not adequately secured.’

According to Francesco Mastrapasqua, president of Assocold, an association representing companies operating in the refrigeration sector (with a turnover of 2 billion and 9,000 employees), the cyber-attacks carried out along the cold chain in several European countries – and, to a lesser extent, in Italia too – must prompt us to be more vigilant regarding the resilience of downstream infrastructure, without, however, taking a step backwards in the adoption of new technologies.

Loading...

In your opinion, what was the vulnerability that allowed the hackers to cause damage to the shops? 

An industrial refrigeration system consists of several components in addition to the machine itself, strictly speaking. These include the electronics that enable it to operate and the retail outlet’s network infrastructure. It is here, as far as we can tell, that the hackers gained access. Remote monitoring is therefore not a risk but an ally in combating such incidents; it is the most effective measure for preventing attacks because it allows for real-time monitoring of parameters. And if a parameter goes out of range – say, to 50 degrees – you notice it straight away.
Il presidente di Assocold

Francesco Mastrapasqua

What can be done to prevent similar incidents in the future?

Of course, there is no such thing as zero risk, but it is possible to take steps to significantly mitigate the scale of the problems. A first general consideration concerns investment in cybersecurity, which must be a top priority, involving secure architectures, safe remote access and adequate VPN-based network protection systems. What has happened must not cause the market to take a step backwards in technological terms, but rather to ensure the constant updating of technologies. The most obsolete systems, containing families of components that are no longer in production, are the most vulnerable in this regard, and I believe it would be useful to introduce a round of incentives to facilitate the replacement of these systems, some of which date back 15–20 years. That said, when we compare what happened in France – where 700 shops were affected – with the situation in Italia, we see a much more resilient national system.

How are new digital technologies changing your sector? 

Whilst in some respects – such as the types of gas used or mechanical operation – innovations are merely incremental, the digital sphere is, in fact, where innovation is advancing at lightning speed. Remote monitoring, which large retail chains often stipulate in their specifications, makes it possible, for example, to carry out maintenance before breakdowns occur. Or to improve efficiency by managing parameters in response to what is happening in-store. For example, by reducing ventilation when there is a massive influx of goods, whilst the doors of the refrigerated display cabinets are open. Unlike in the past, with artificial intelligence, the millions of data points collected in the field can be utilised and translated into concrete actions. All of this translates into efficiency and, consequently, competitiveness for the end customer. For large retail chains, this is now the path they have taken, whilst smaller retailers are more cautious. But in general, I believe that is where the future lies.

Given the proliferation of risks and attacks, European regulations are also shifting in this direction, raising digital security standards. Do you agree with this approach?

Certainly. Here we see a set of rules – I’m thinking of the Cyber Resilience Act – which introduces mandatory cybersecurity requirements for all hardware and software products containing digital components sold in the EU. These rules evolve in step with technological changes and impose specific responsibilities regarding the security of systems, whilst promoting closer collaboration throughout the entire value chain.

Copyright reserved ©
Loading...
Loading...

Brand connect

Loading...

Newsletter

Notizie e approfondimenti sugli avvenimenti politici, economici e finanziari.

Iscriviti