
The link between Everest’s pro-Russian faction and the cyberattack on the Brenner Pass
Specialising in data theft, they are threatening to publish the information online

Key points
Strategic infrastructure hubs – particularly in terms of trade and logistics – such as the Brenner Tunnel, but also the dissemination on the dark web of personal data belonging to institutional representatives by pro-Russian hackers and, of course, the chaos affecting flights. The fronts in this hybrid war are multiplying. With every passing hour, security against cyber-attacks is becoming a top priority for governments. The strategies deployed must be comprehensive, with the aim of, at best, eliminating and, at worst, containing the impact on citizens and the civilian population.
The case of the Brenner Base Tunnel
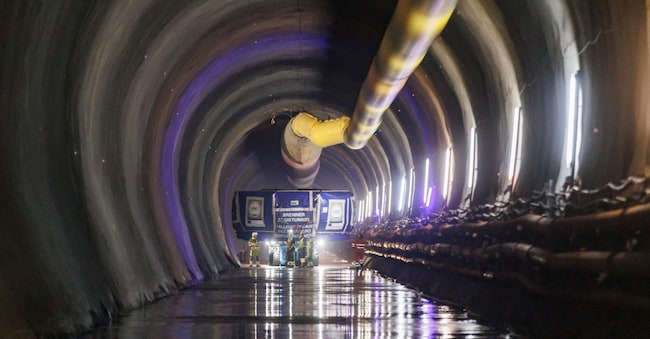
The latest incident involved Bbt Se: the European public limited company responsible for the design and construction of the Brenner Base Tunnel was the target of a targeted cyber-attack on 17 October. The investigation has been entrusted to the Bolzano Postal Police and is still ongoing. The attack is believed to have targeted data not accessible to the public, which was stolen by unauthorised individuals via the internet.
Bbt Se added that the incident did not, and does not, pose any risk to the work currently underway, and has had no impact on the company’s operational activities. As reported by the Austrian newspaper Tiroler Tageszeitung, the group known as ‘Everest’, linked to the Russian-speaking cybercrime scene, is said to be under investigation. This is an international extortion network specialising in data theft, threats to publish data online, and demands for money in exchange for silence.
The Russian lead
There is also another line of inquiry. Following days of alerts that forced aircraft to divert and caused delays, European intelligence services are pursuing the Russian lead. According to the Financial Times, a cross-border investigation is under way to trace the origin of the alerts: some intelligence officials consider Russia the most likely culprit, in light of the motive, the modus operandi, past precedents and the initial evidence gathered. Among the hypotheses being examined are the actions of pro-Kremlin activists or hacker groups. However, attributing the threats to Moscow remains far from a foregone conclusion.
Investigators warn that identifying those responsible could take a long time, without necessarily leading to a definitive conclusion. Meanwhile, the FBI has also joined the network of information-sharing between police forces. According to the Portuguese radio station Observador, it was the US investigative agency that sent three alerts to the Lisbon police on Friday: one concerning the Ryanair flight from Lisbon to Rome and two concerning TAP flights bound for Paris and Copenhagen.


